Cybersecurity
Building a Layered Defense Strategy to Guard Your Enterprise
One security tool isn't a strategy. Learn how to stack independent controls from perimeter to data core so that no single failure means total compromise.
One security tool isn't a strategy. Learn how to stack independent controls from perimeter to data core so that no single failure means total compromise.
Behavioral blocking monitors program actions instead of matching signatures, catching zero-day exploits and fileless malware that traditional tools miss.
Threat intelligence feeds deliver IOCs, malicious domains, and file hashes in real time. These 10 feeds are essential for any SOC defending against malware.
Deploying antivirus across an enterprise takes more than clicking install. This guide covers ring deployment, EPP vs EDR selection, and phased rollout.
Most breaches start at the endpoint. This comprehensive guide covers EDR, MDR, XDR, next-gen antivirus, and the hardening strategies enterprises need now.

The 2026 Verizon DBIR confirms a historic shift: vulnerability exploitation has overtaken credential theft as the top initial access vector. Attackers are moving faster than organizations can patch — and the gap is widening.
The login form is the most attacked surface on the web. Here's how to implement form-based authentication correctly with modern security controls.
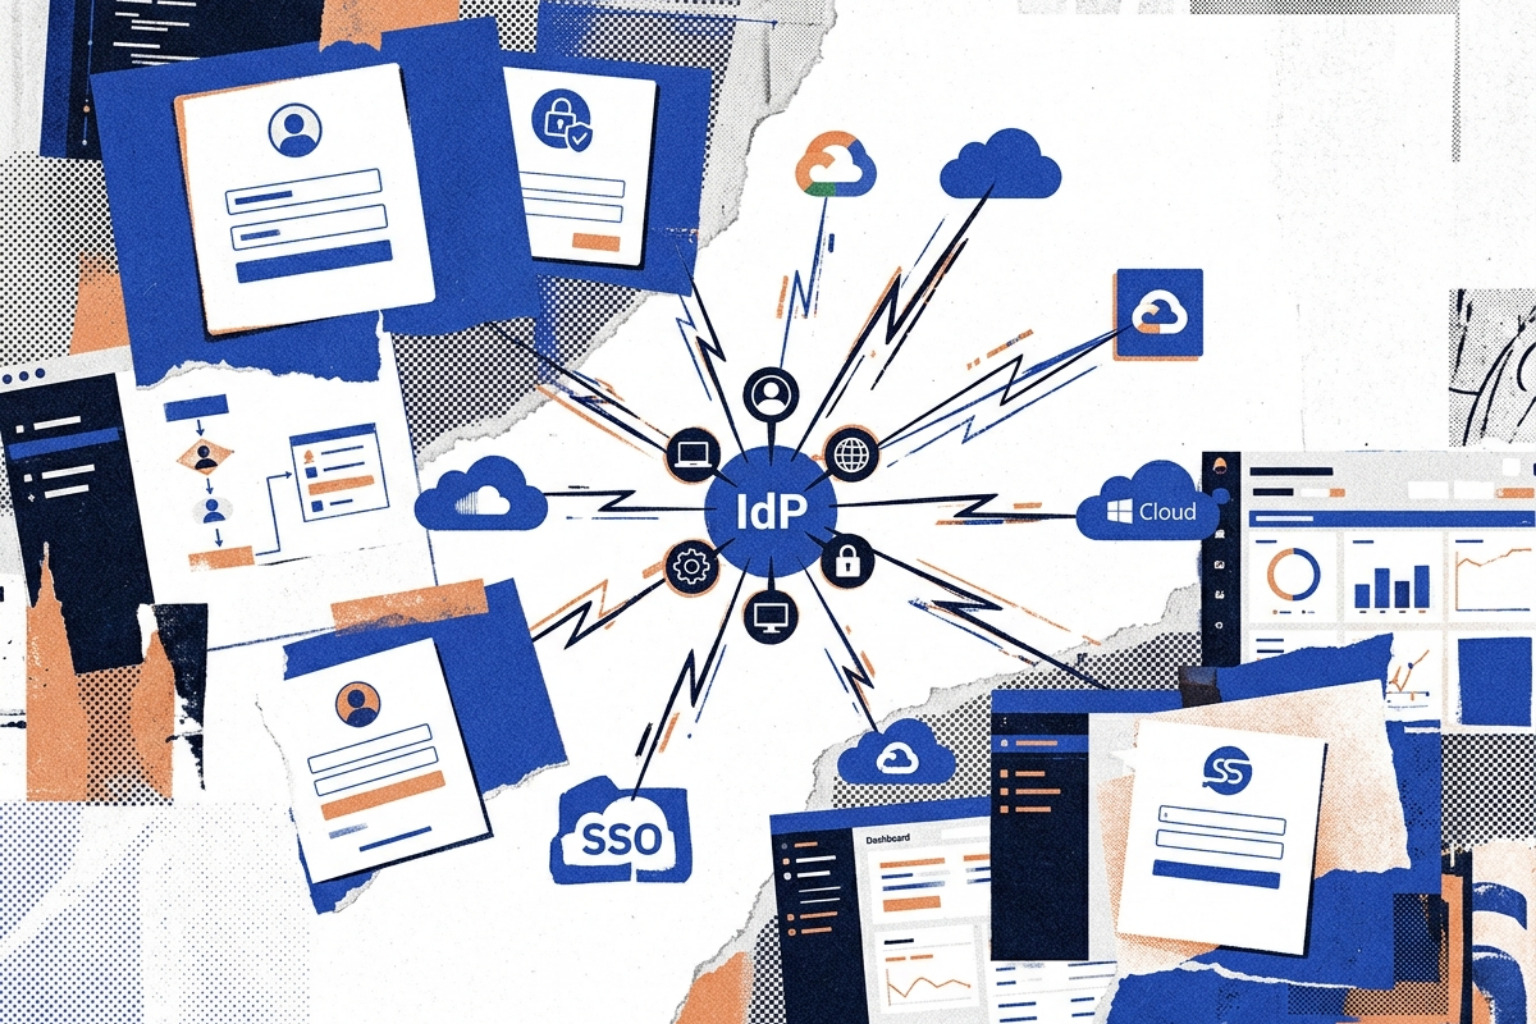
Federated identity management lets users log in once and access services across organizational boundaries. Here's how the protocols and trust models work.
Everything you need to choose and configure a 2 factor authenticator: from how TOTP codes are generated to comparing cloud-synced apps, hardware tokens, and when to migrate to FIDO2 passkeys.